What’s the creepiest thing your phone has ever done? In my case, I was talking with my friend about buying a pair of shoes, and that same pair greeted me with an ad as soon as I opened my Instagram. Just a bit too eerie for a mere coincidence.
Now, repeat that across hundreds of daily actions: searches, location check-ins, video clicks, and messages, and those individual actions stop being so private. Just like a jigsaw puzzle, the pieces fit and reveal a pretty detailed version of your daily life. Modern personal data is no longer just static information like a phone number or mailing address. It is something you constantly update through behaviour, which leaves us with a serious problem: how much control do you actually have over the data you create?
This conflict isn’t brand new. Back in 1890, legal scholars Samuel Warren and Louis Brandeis published “The Right to Privacy” in the Harvard Law Review, arguing that new photography techniques and rapid newspaper publishing needed new rules for protecting personal life. That famously became the core definition of privacy law: “the right to be left alone.”
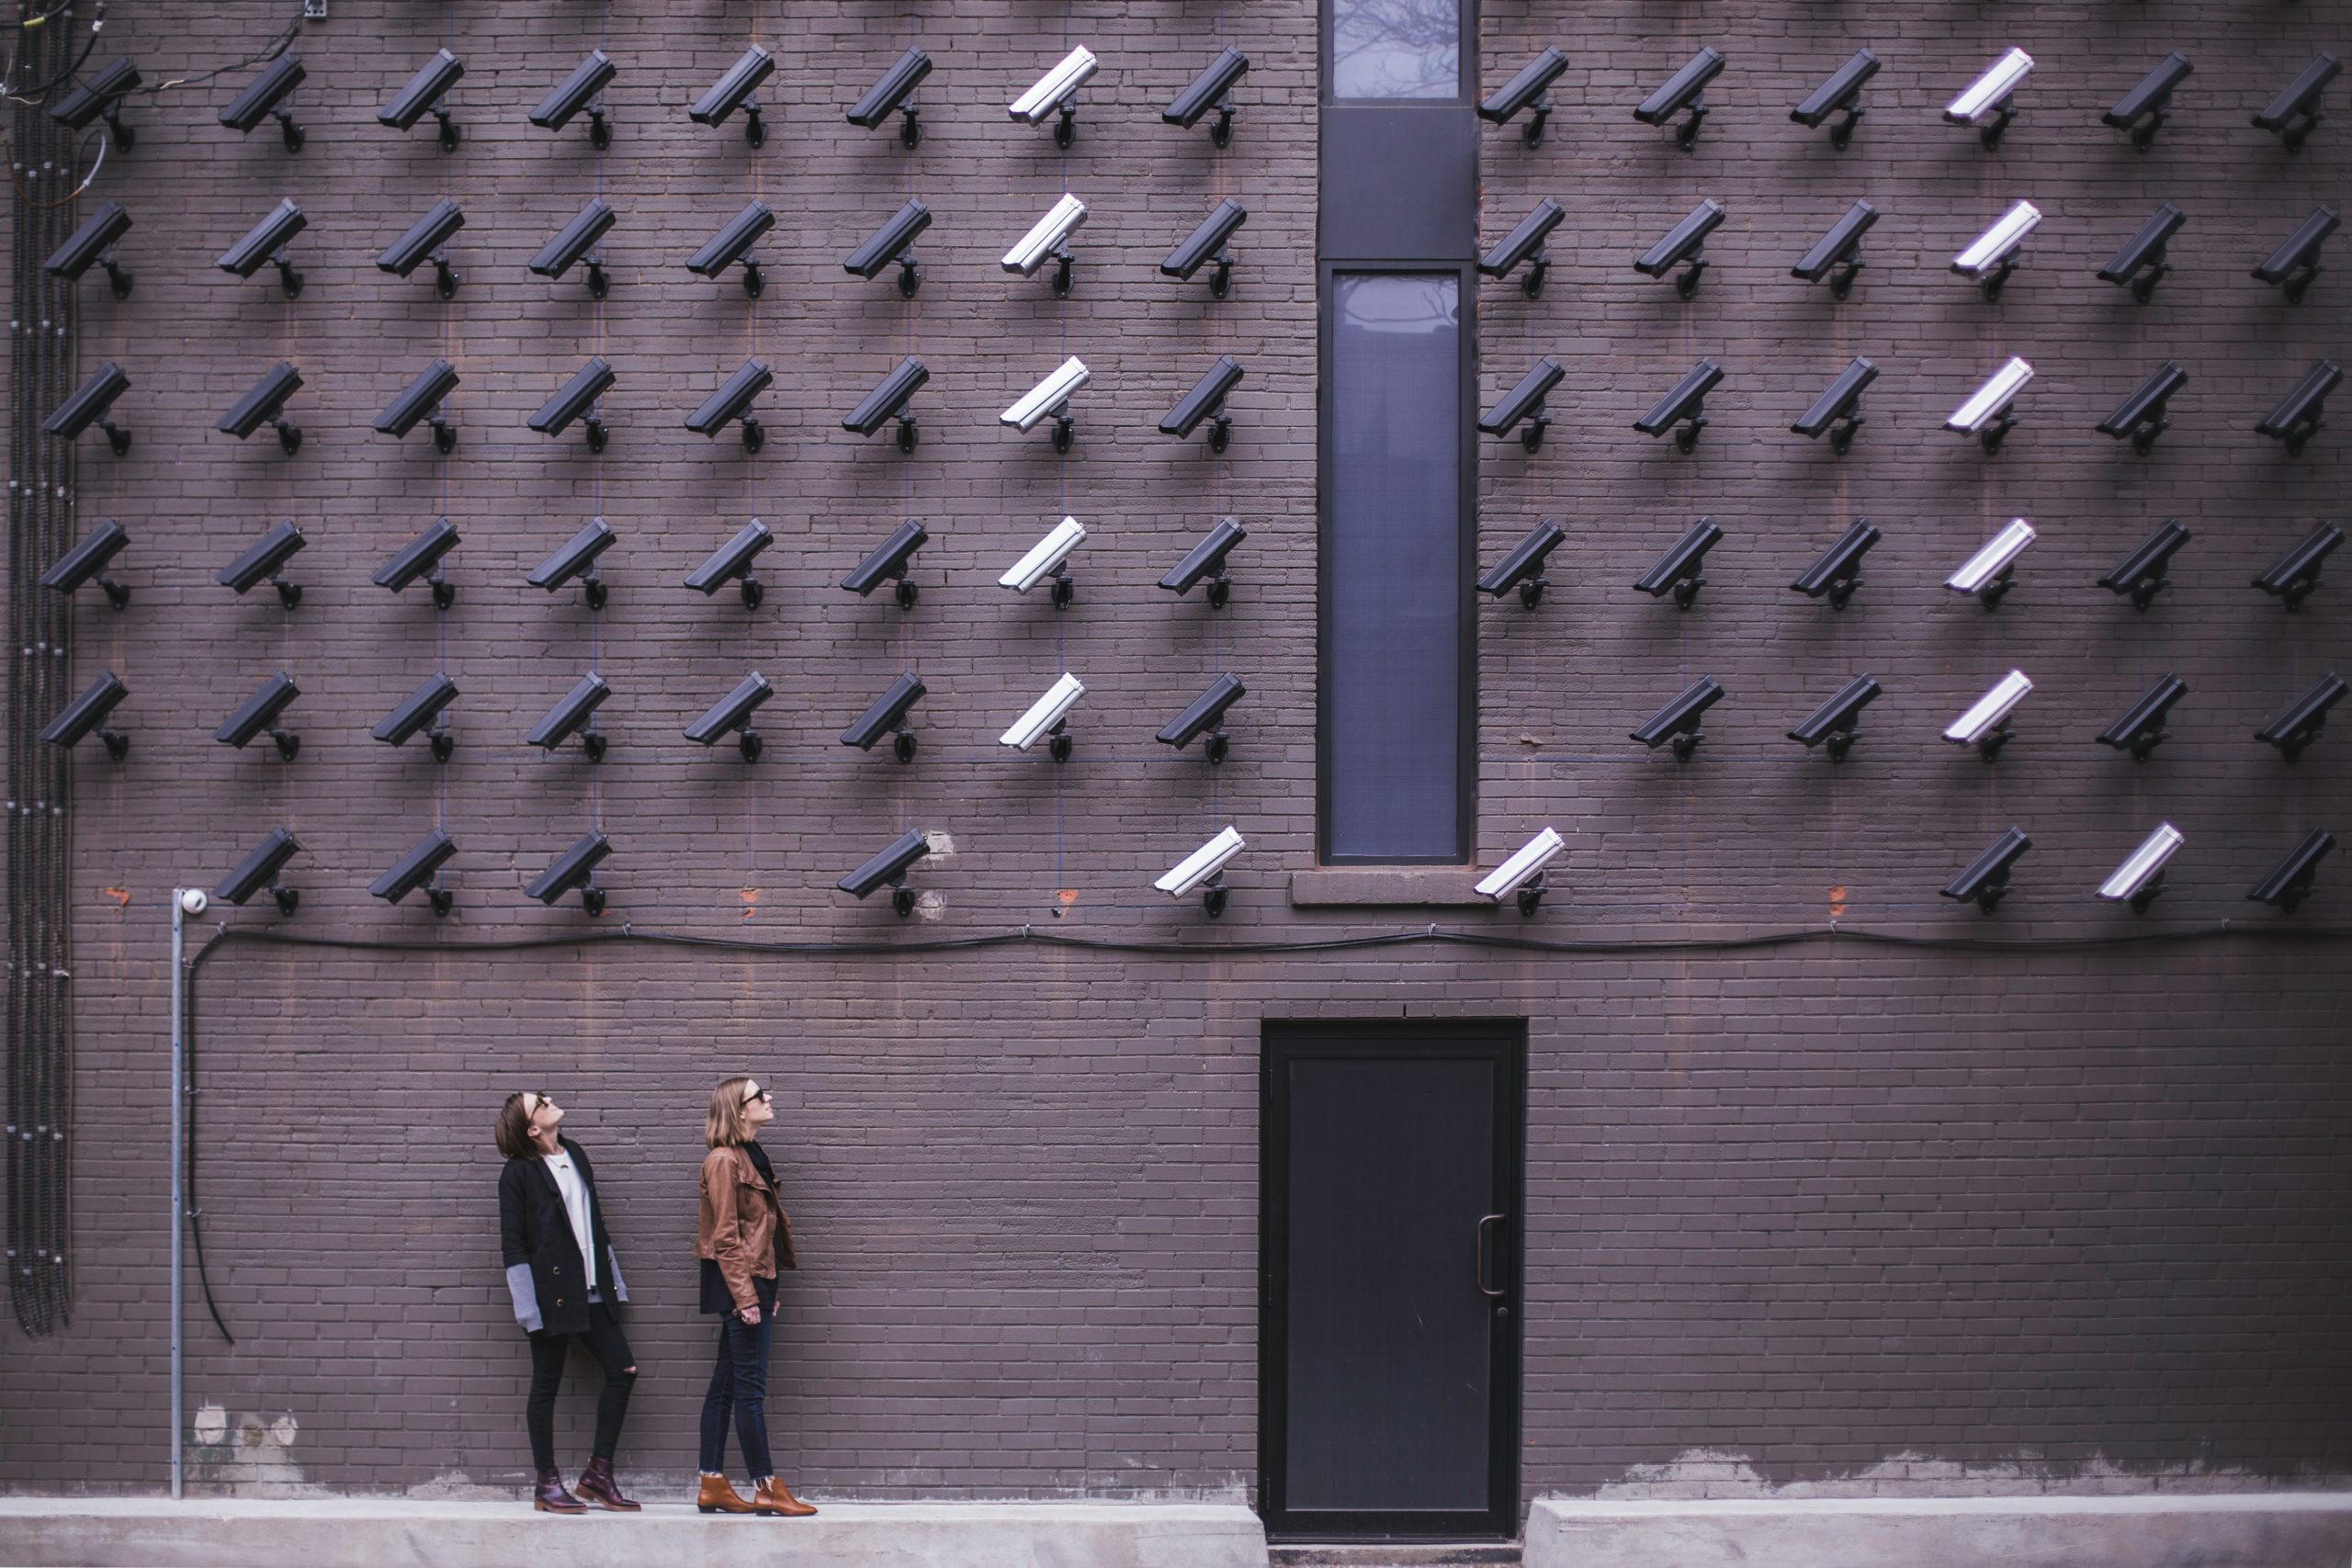
Today, that boundary has slowly faded. A 2024 Federal Trade Commission report detailed how major streaming and social media platforms collect massive amounts of data from users and non-users alike, combining third-party data brokers with tracking tools to profile consumers. For the average person, the choice is mostly fake: click “Agree” or get cut off from modern digital tools. Privacy isn’t just about hiding secrets; it’s about power. Knowing you are constantly monitored subtly changes what you search, how you speak, and what opinions you feel comfortable sharing.
Regulations like Europe’s General Data Protection Regulation (GDPR) attempted to balance the scales by giving people rights to access, correct, transfer, or delete their personal data, while requiring companies to collect only what they strictly need. But in practice, the execution backfired in key ways. Heavy compliance costs hit small businesses, independent publishers, and startups hard, while giant tech companies easily absorbed the expense. Because mega-platforms can still share data across their own products while external transfers face strict limits, the rules didn’t bother them. For consumers, it led to consent fatigue, an endless stream of cookie pop-ups that almost everyone clicks through just to load a webpage, giving the illusion of consent without real control.Stopping data collection entirely isn’t realistic or even desirable. Modern systems depend on data flows: hospitals need medical records, banks need identity checks to stop fraud, and mapping apps need location details. The issue isn’t data collection itself, but unnecessary, excessive, and hidden tracking. Instead of relying on heavy administrative rules that end up protecting monopolies, the solution needs to focus on practical user control: clear transparency, strict limits on how long data can be kept, and simple, instant ways to revoke consent.
Every click and search creates a record that usually outlives the moment that produced it. Technology should exist as a practical tool that serves human needs, not an invisible tracking network steering our choices. Reclaiming control over your digital identity shouldn’t mean jumping through endless regulatory hoops or clicking dozens of pop-up banners every day; it means building systems that respect user boundaries by default.